> For the complete documentation index, see [llms.txt](https://docs.usepylon.com/pylon-docs/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.usepylon.com/pylon-docs/platform/roles-and-user-management.md).
# Roles & User Management
What Admins, Members, and Viewers can do, how to invite, deactivate, and reactivate users, and how to build custom roles.
Every Pylon user has one role, and the role controls what they can see and change. Manage users in **Settings > Workspace > Users**. Manage roles in **Settings > Workspace > Users > Manage User Data > Roles**.
## Roles
| Role | Who it's for |
| -------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------ |
| **Admin** | People who run the workspace: settings, billing, users, roles, integrations, and API tokens. |
| **Member** | Day-to-day support work. Most of your team should be Members. |
| **Viewer** | Read-only access for people who need to look things up and leave internal notes, but not work issues. Available on select plans — contact your account team. |
| **Integration User** | People who use Pylon only through an integration such as Slack or Linear. They can't sign in to Pylon. |
| Custom roles | Roles you build yourself. Available on the Enterprise plan. See [Custom roles](#setup). |
### What Admins, Members, and Viewers can do
| Capability | Admin | Member | Viewer |
| ----------------------------------------------------------------------------------------------- | ----- | ---------------------------- | --------- |
| View issues, accounts, contacts, call recordings, and knowledge base articles | Yes | Yes | Yes |
| Leave internal notes on issues | Yes | Yes | Yes |
| Use Ask AI | Yes | Yes | Yes |
| Reply to customers and update issues (assignee, status, fields) | Yes | Yes | No |
| Mark issues as spam | Yes | Yes | No |
| Edit accounts, contacts, tasks, and feature requests | Yes | Yes | No |
| Delete issues, accounts, contacts, and call recordings | Yes | No | No |
| Create and edit knowledge base articles and collections | Yes | Yes | No |
| Publish and unpublish articles, and change knowledge base admin settings such as custom domains | Yes | No | No |
| Configure email, chat widget, ticket forms, customer portal, triggers, custom fields, and tags | Yes | Yes | View only |
| Edit macros | All | Only macros shared with them | View only |
| Analytics, reports, and broadcasts | Yes | Yes | View only |
| Manage AI support agents and skills | Yes | Yes | No |
| Manage webhooks and warehouse syncs | Yes | Yes | View only |
| Use the Pylon MCP and connect MCP servers | Yes | Yes | No |
| Install and manage integrations, custom apps, and codebase tools | Yes | No | No |
| Workspace, billing, and data retention settings | Yes | No | No |
| Invite users, change roles, and deactivate users | Yes | No | No |
| Create API tokens and bots | Yes | No | No |
| Create custom roles and configure sign-in, SSO, and SCIM | Yes | No | No |
The built-in roles can't be edited. To start from one and change it, [duplicate it into a custom role](#setup).
### Admin
Admins can do everything in Pylon. Some actions are Admin-only and can't be given to any custom role:
* Inviting users, changing roles, changing sign-in methods, and deactivating users
* Creating, editing, and deleting custom roles, and setting the default role
* Creating API tokens and bots
* Bulk adding users to Slack channels
Your workspace always needs at least one Admin, so Pylon won't let you change the role of the last Admin. If an Admin created API tokens with the Admin role, delete those tokens before changing that Admin's role.
### Member
Members can do almost all support work: reply to customers, update and route issues, edit accounts and contacts, write knowledge base articles, and configure most support settings. Members can't delete records, publish knowledge base articles, install integrations, change workspace or billing settings, or manage users and roles.
Members and Admins have **MCP Access**, which lets them use the [Pylon MCP](/pylon-docs/integrations/pylon-mcp.md).
To let someone publish articles or delete issues without making them an Admin, use a [custom role](#setup).
### Viewer
Viewers can see issues, accounts, contacts, the knowledge base, analytics, and most settings, but can't change them. They can leave internal notes on issues and ask questions in Ask AI. They can't reply to customers.
The Viewer role appears in role pickers only if your plan includes Viewer seats or custom roles.
### Integration User
Integration Users are people who interact with Pylon through an integration, for example a teammate who links Linear issues from Slack, but who don't need the Pylon app. They can't sign in. Setting someone's role to **Integration User** turns off their sign-in. Find them under the **Integration Users** view on the Users page.
## Manage users
Go to **Settings > Workspace > Users**. Use the views at the top to switch between **Pylon Users**, **Integration Users**, **Bots**, and **All Users**. Use **Export to CSV** to download the current list.
### Invite users
{% hint style="info" %}
Only Admins can invite users. If SCIM is turned on, add users in your identity provider instead.
{% endhint %}
1. Click **Invite User**.
2. Choose **Select existing users** to pick people from your connected Slack workspace, or **New user** to enter a full name and email address.
3. Pick a **Role**. It starts on your workspace's [default role](#sso).
4. Click **Invite**.
If an email address isn't on one of your organization's domains, Pylon warns you so you don't invite a customer by mistake.
### Change roles and other settings
* Change one user's role from the **Role** column, or open the user and change it there.
* To edit several users at once, select them and use the bar that appears to change their **Role** or **Sign-in method**, **Add to team**, **Assign Support Hours**, or set their **Status**.
Only Admins can change roles and sign-in methods.
### Remove a user (deactivate)
Pylon doesn't permanently delete users. To remove someone, deactivate them. This removes their access and keeps their past messages, notes, and activity.
1. On the Users page, click the user's name.
2. Click **Deactivate**, then confirm.
3. If they have open issues, choose who to reassign them to: a teammate or **Unassigned**. With **Unassigned**, you can also check **Refresh or update team assignment** to move the issues to a team, or pick **Current Team** to keep their team and rerun its assignment strategy.
4. Click **Save**. Reassignment can take a minute and can't be undone.
When you deactivate a user:
* They can't sign in.
* API tokens they created, and tokens that act as them, are permanently deleted. The confirmation dialog lists them. Anything using those tokens stops working, so create replacement tokens first. A [bot](#bot-users) is a good owner for long-lived tokens.
* Any open issues you don't reassign stay assigned to them.
* They're removed from team schedules, and the skills assigned to them on [teams](/pylon-docs/platform/teams.md) are removed.
* They no longer appear on the Users page.
To move someone's open issues without deactivating them, open the user and click **Reassign issues**.
{% hint style="warning" %}
If SCIM is turned on, deactivate SCIM-provisioned users in your identity provider. The **Deactivate** button is turned off for them in Pylon.
{% endhint %}
### Reactivate a user
1. On the Users page, open the **...** menu at the top right and choose **Reactivate User**.
2. Select one or more deactivated users.
3. Click **Reactivate**.
API tokens deleted during deactivation aren't restored.
### Bot users
A bot is an identity for API tokens, so automated traffic is attributed to the bot instead of a teammate. Bots can't sign in.
1. On the Users page, open the **Bots** view and click **New Bot**. Only Admins can create bots.
2. Enter a name, optionally upload a square avatar, and pick a **Role**. API tokens acting as the bot use this role.
3. Click **Create Bot**.
Then create a token that acts as the bot. See [Authentication](/pylon-docs/developer/api/authentication.md).
Deactivating a bot permanently revokes every API token acting as it. Reactivating the bot doesn't restore those tokens.
## Custom roles
Custom roles let you choose exactly what a group of users can do, down to which issues and accounts they can see. Custom roles are available on the Enterprise plan. Without it, the Roles page shows an upgrade banner.
{% hint style="info" %}
Only Admins can create, edit, or delete roles.
{% endhint %}
### Create a role
1. Go to **Settings > Workspace > Users**, click **Manage User Data**, and open the **Roles** tab.
2. Click **Create**, or open the **...** menu on an existing role and choose **Duplicate**.
3. Enter a **Role Name**.
4. Set an access level for each permission (see [Permissions](#permissions)).
5. Click **Create**.
Duplicating Admin leaves out the [Admin-only actions](#admin-permissions-4). If a role has no access to Accounts or Issues, Pylon warns that the role may have a broken experience.
To delete a custom role, open its **...** menu and choose **Delete**. You can't delete a role that's assigned to active users or API tokens, or that's set as the default role. Deactivated users who had the role move to the default role.
### Limit which issues a role can access
The **Issues** card on a custom role controls issue access with groups:
1. Click **Add Group**, then **Add Filter** to set the conditions, such as source, team, tag, or support email address.
2. Pick the group's access level: **No access**, **View only**, **Full access**, or **Custom access**. Custom access lets the role view matching issues plus any of **Add notes**, **Edit** (reply and update), **Delete**, and **Mark as spam**.
3. Set **Default** access for issues that match no group.
Pylon checks groups from top to bottom and applies the first one that matches, so put the most specific groups first. Drag groups to reorder them, or use a group's menu to duplicate or delete it.
For example, a `Security` role could have one group for issues sent to your security email address with **Full access**, and **Default** set to **No access**.
### Limit which accounts a role can access
Under **Accounts**, use **Refine access scope with filters** to limit the role to accounts that match your filters, such as account owner, type, tag, or a custom field.
### Knowledge base publishing
The Knowledge Base permissions are separate:
* **Articles & Collections**: view or edit articles and collections.
* **Publish articles**: publish and unpublish articles.
* **Admin settings**: manage sensitive settings such as custom domains.
You can limit **Publish articles** and **Admin settings** to specific collections with **Refine access scope with filters**. Members can edit articles but not publish them, so use a custom role to give writers publishing rights.
### Permissions
Most permissions have levels: **No access**, **View**, and **Full access**, plus **Edit** for permissions that also allow deleting. Issues adds **Notes** and **Reply**. Macros uses **View**, **Write**, and **Full access**, where Full access lets the role edit every macro, including ones not shared with them. A few permissions are a single **Enabled**/**Disabled** switch.
| Category | Permissions |
| ---------------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Objects | Accounts, Contacts, Custom objects\*, Issues, Tasks, Call Recordings, Account notebooks, Feature Requests |
| Organization | Workspace |
| User Management | Users (role changes still require Admin), Teams |
| General Features | Analytics, Reports, Broadcasts, Integrations, Support agents\*, Skills\*, Ask AI\* |
| Support Features | Email, Update email suppressions, Chat Widget, Phone\*, SMS\*, Support Workflows, Active Times\*, Operations Automation, Ticket forms, Customer Portal, Triggers, Macros, Issue Custom Fields, Account Custom Fields, Contact Custom Fields, Issue Tags, Account Tags |
| Knowledge Base | Articles & Collections, Publish articles, Admin settings |
| Developer | Custom Apps, Codebase Tools, Webhooks, Warehouse Sync, MCP Access, MCP connections |
| Security | Data Retention |
\* Shown only when your workspace has that feature.
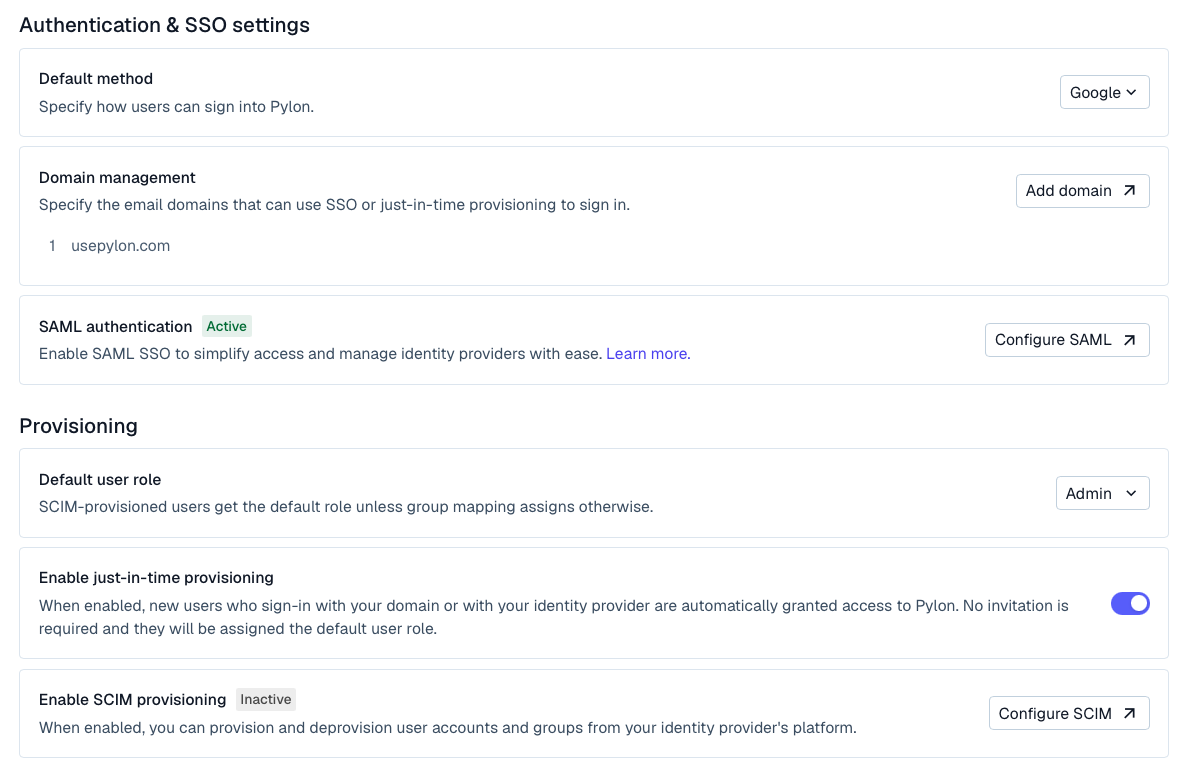
## Sign-in, SSO, and SCIM
Admins manage sign-in and provisioning in **Settings > Workspace > Access**. The page is called **Access & SSO** when your plan includes SAML. SAML SSO and SCIM are available on select plans — contact your account team.
* **Sign-in methods**: choose how new users can sign in: Slack, Google, Microsoft, or SAML. Existing users keep their current method. To change it, use the **Sign-in method** column on the Users page. Signing in with Slack uses your Slack workspace's login, including any SSO you've set up for Slack.
* **Domain management**: the email domains that can use SSO or just-in-time provisioning. With SAML, click **Add domain** to verify a new domain. Otherwise, contact support to change domains.
* **SAML authentication**: click **Configure SAML** to connect your identity provider, such as Okta, Microsoft Entra ID, or Google Workspace.
* **Default user role**: the role new users get.
* **Enable just-in-time provisioning**: when on, anyone who signs in with one of your domains gets access without an invitation and is given the default user role.
### SCIM
SCIM lets your IT team provision and deprovision Pylon users from your identity provider.
1. Set up SAML and confirm **SAML authentication** shows **Active**.
2. Under **Provisioning**, click **Configure SCIM** and connect your directory.
3. Optionally, under **SCIM group to Pylon user role mapping**, click **Add mapping** to give each SCIM group a role. Users who aren't in a mapped group get the default user role.
When SCIM is on, your identity provider manages users: **Invite User** is turned off, roles come from group mapping or the default role, and SCIM-provisioned users must be deactivated in the identity provider. You can still deactivate users that SCIM didn't provision directly in Pylon.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.usepylon.com/pylon-docs/platform/roles-and-user-management.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.